Security Overview
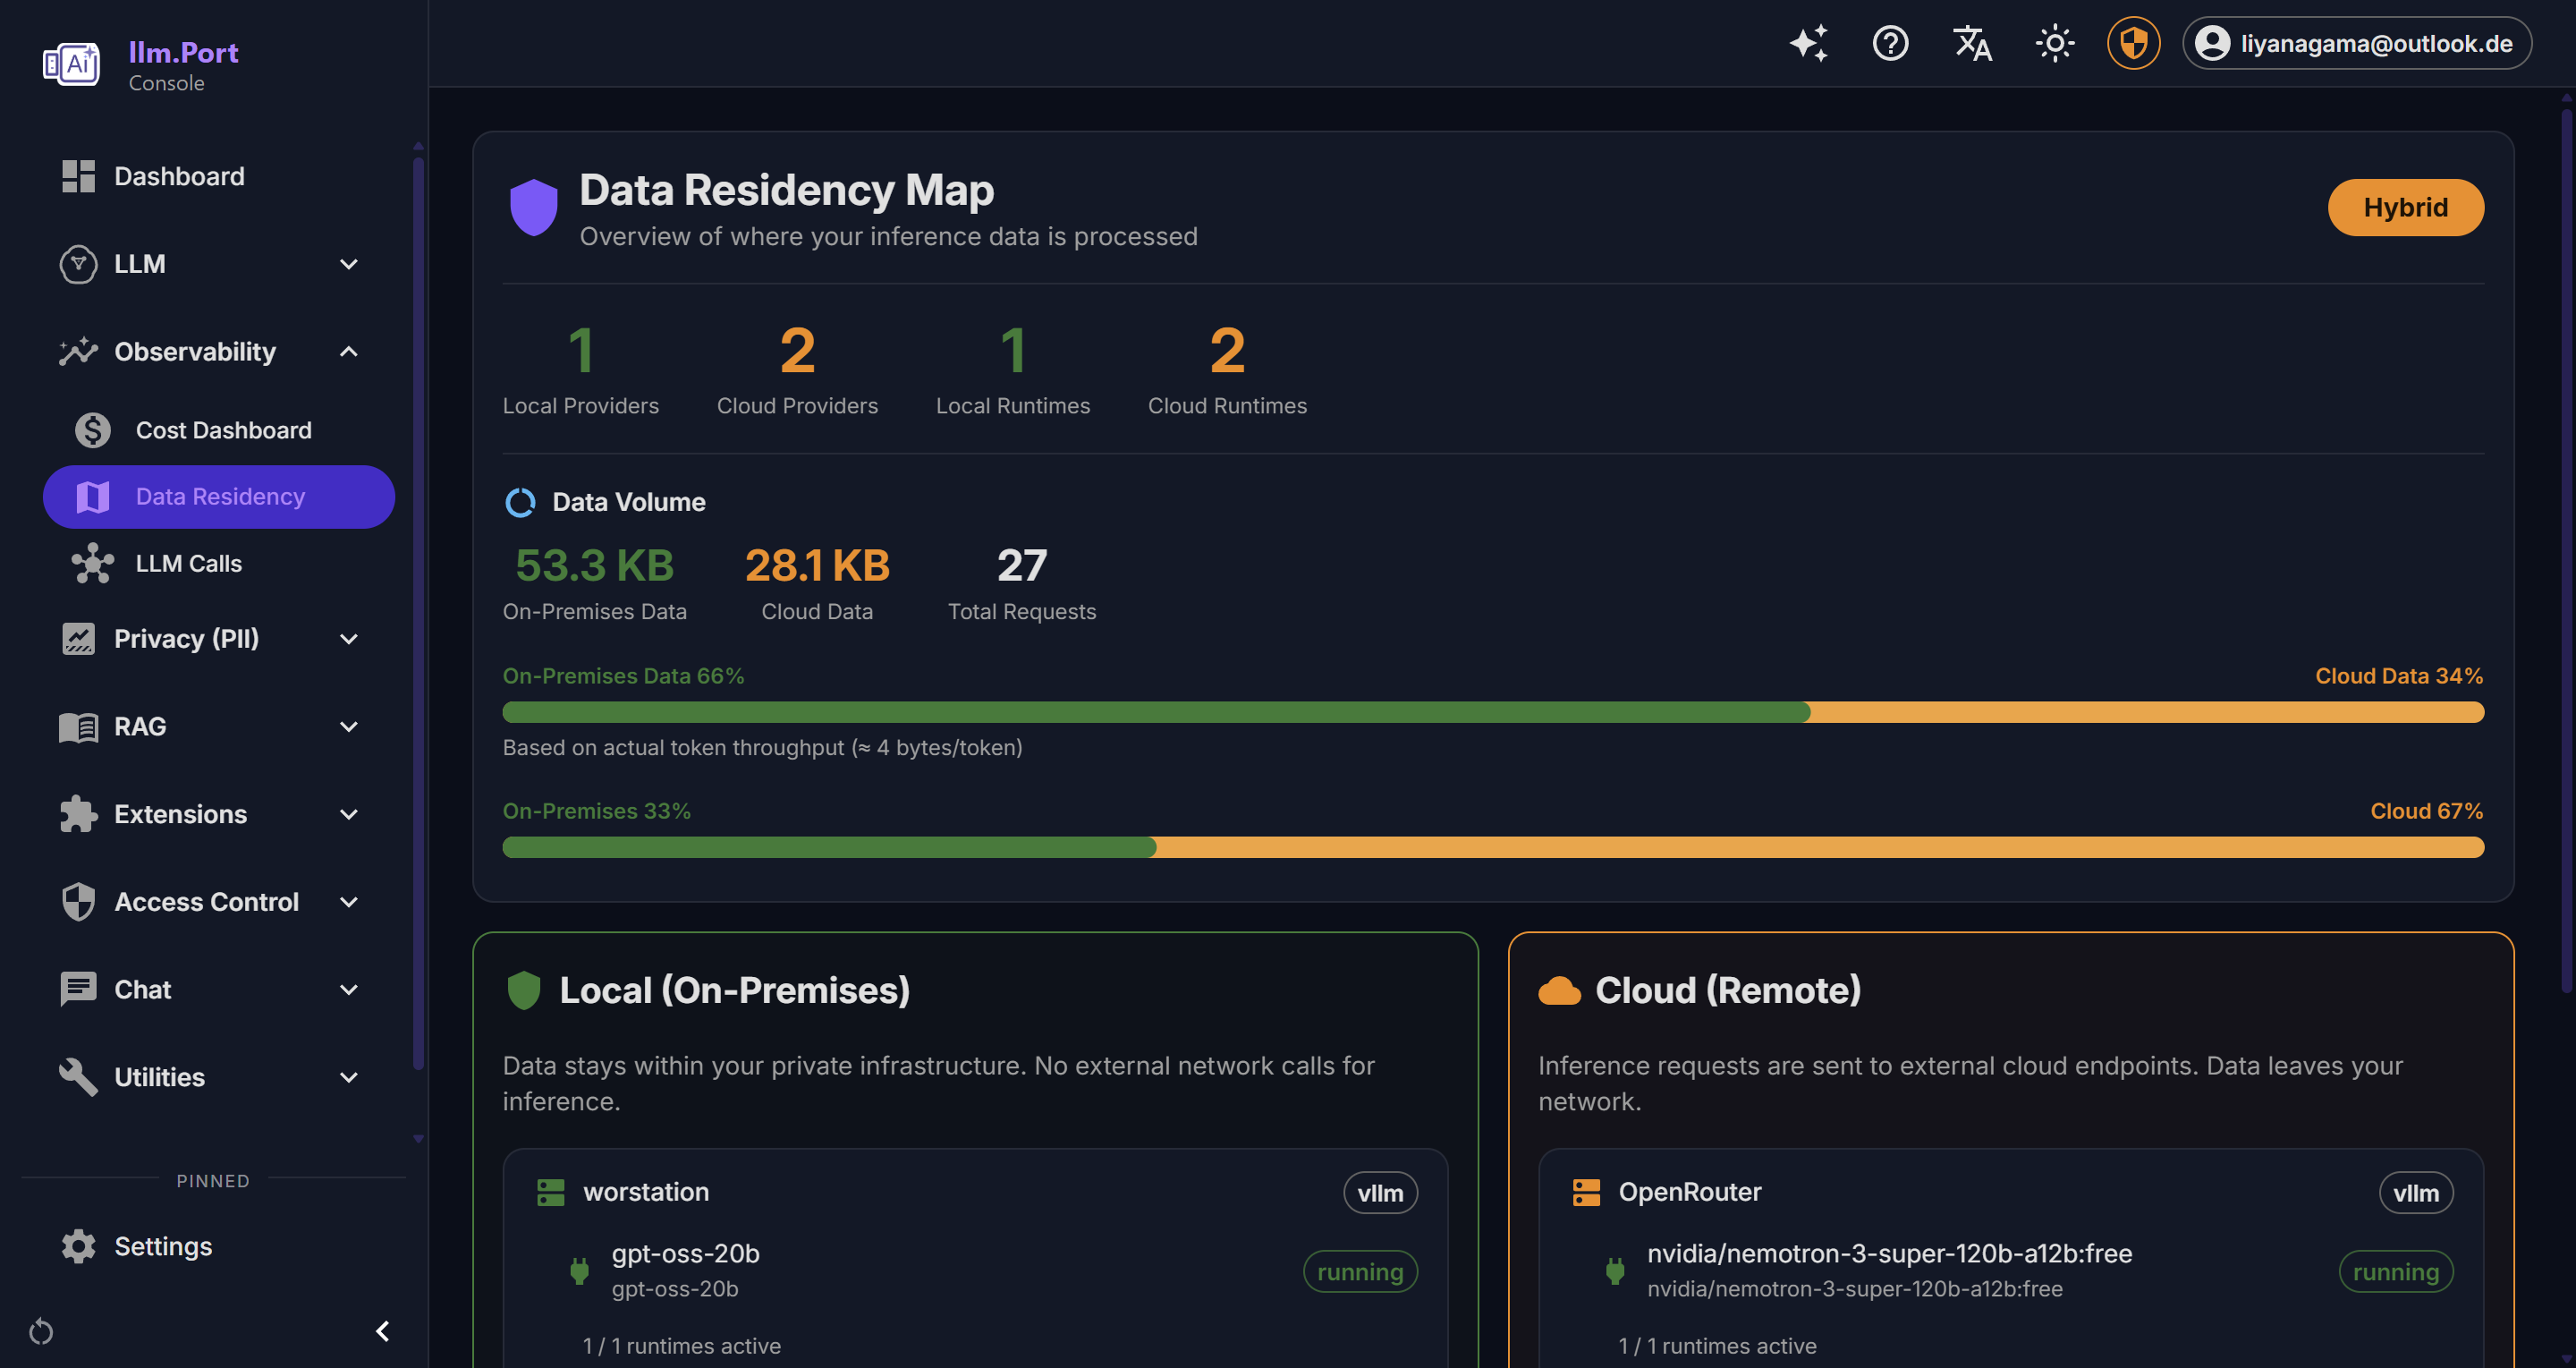
llm.port includes layered controls for authentication, authorization, policy enforcement, and audit visibility.
Core controls
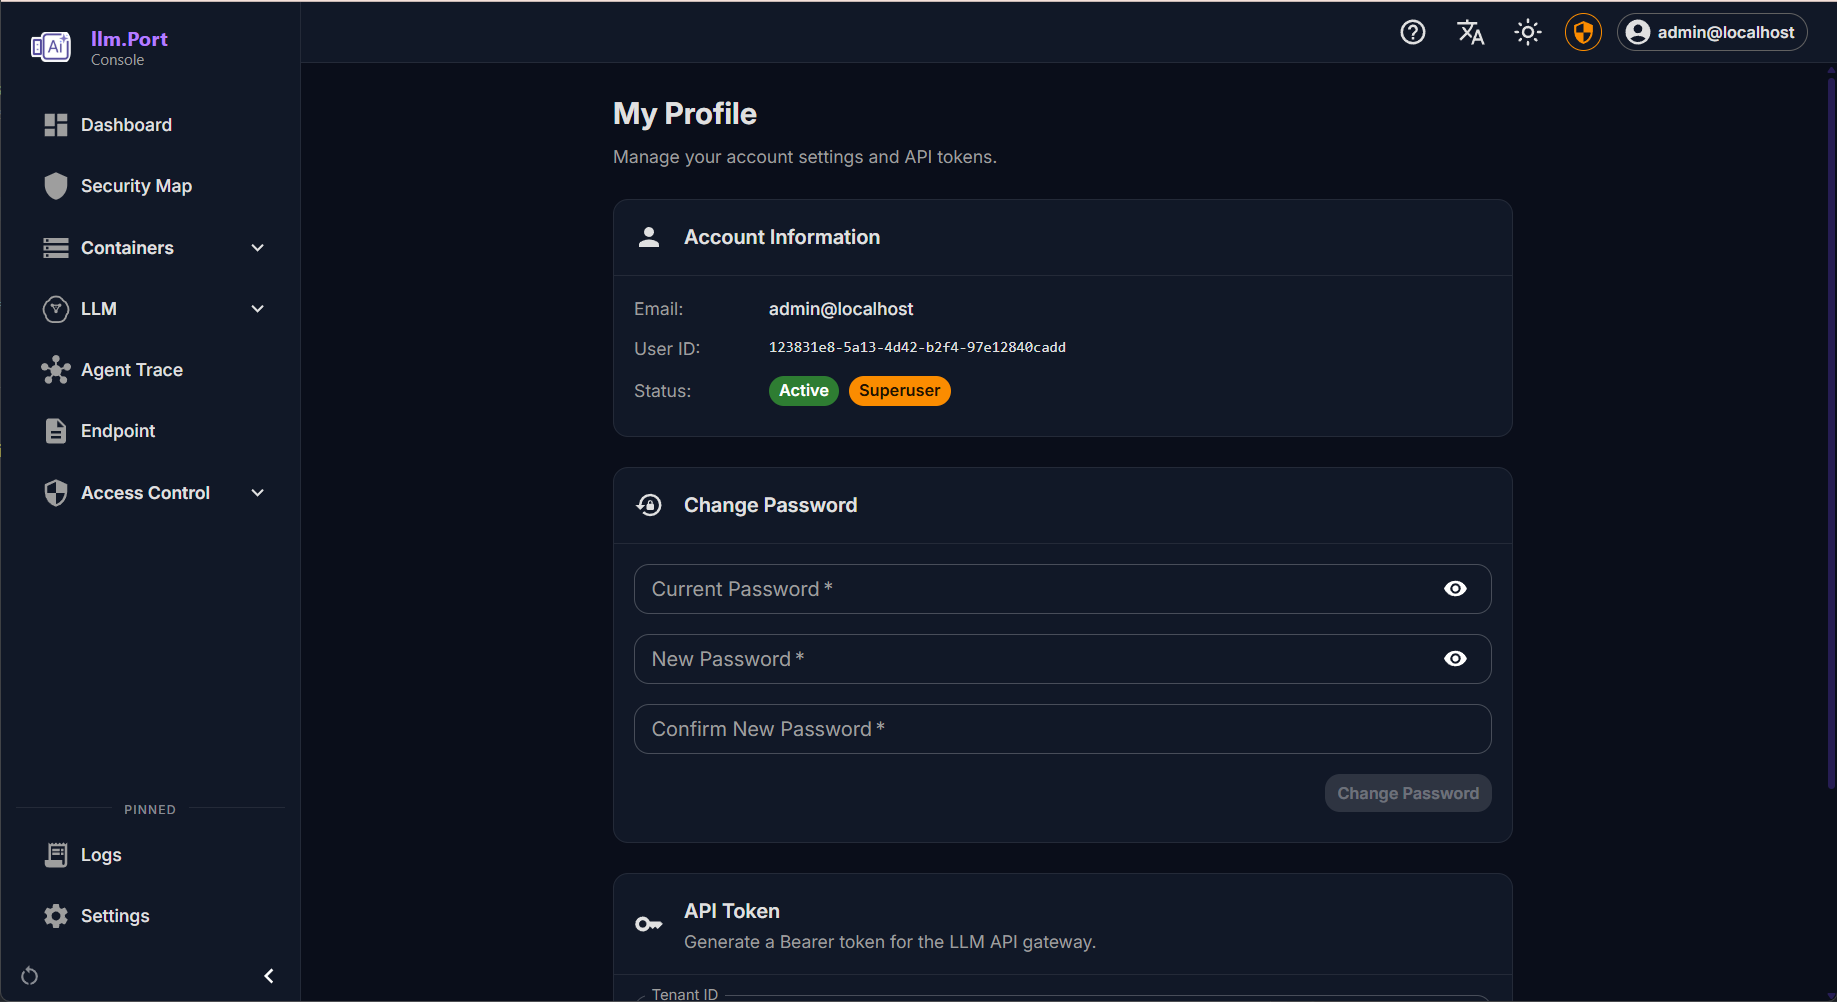
- Token-based API authentication
- Role-based access controls for administrative and operational actions
- Configurable policy enforcement for model access and usage boundaries
- Audit-friendly operational visibility
Security outcomes
- Controlled access to AI workloads
- Reduced risk of unauthorized configuration changes
- Better traceability for compliance and incident review
Recommended baseline
- Enforce strong credential management
- Separate environments (dev, staging, production)
- Apply least-privilege role assignments
- Periodically review access and policy posture
Additional trust pages
Screenshots